
 Client area
Permissions ACE on FiveM: the complete guide to securing your server
FiveM ACE permissions decide who can do what on your FiveM server. They give admin commands to your staff, keep a menu for the police and protect sensitive commands. This guide explains how the ACE system works, gives configurations you can copy and shows how to test them to secure your server.
Permissions go in the server.cfg file, which you edit from OuiPanel, the OuiHeberg game panel. They are written the same way on both FiveM editions offered in OuiPanel, Legacy and Enhanced. Only the txAdmin part is limited to Legacy.
What exactly is the ACE system?
ACE (Access Control Entry) is the permission system built into FiveM. With it, you can:
control access to commands and to the features of your scripts;
create groups with different levels of rights;
make one group inherit from another, so an admin also gets a moderator's rights;
protect sensitive commands and resources.
Everything is set in your server's server.cfg file. For a quick test, you can also type the same lines in the console.
The three concepts to understand
Three ideas are enough to read any permission line.
The principal is the identity
The principal is a player or a group. For a player, it is one of their identifiers, prefixed with identifier.. For a group, it is its name, prefixed with group..
identifier.steam:110000xxxxxx    # Steam identifier
identifier.license:xxxxxx        # Rockstar license
identifier.discord:xxxxxx        # Discord ID
identifier.fivem:xxxxxx          # FiveM ID (Cfx.re account)
group.admin                      # A group
FiveM also provides the builtin.everyone principal. It means everyone, including you.
The ACE is the permission
An ACE applies to an object, which you allow or deny. A command is written command. followed by its name. Other objects use whatever name the script that checks them gives them.
command.kick          # Kick permission
command.ban           # Ban permission
police.armory         # Object checked by a script
An object also covers everything that starts with its name followed by a dot. So command covers every command, and police covers both police.menu and police.armory. Case does not matter, because FiveM turns everything into lowercase.
Allow and deny
You allow (allow) or deny (deny) an object to a principal. When a player acts, FiveM gathers their identifiers, their groups and the groups those inherit from. It then reads the rules set on the object and on its parents.
If it finds a single
deny, the action is refused, whatever theallowrules say.Otherwise, a single
allowis enough to permit it.With no rule at all, the action is refused. A player has no rights until you give them some.
A
denyset onbuiltin.everyoneapplies to everyone, your admins included. Noallowcan lift it.
Inheritance between groups
This is what makes the ACE system so handy. A group can inherit the permissions of another group. Take this hierarchy.
superadmin → admin → moderator → support
A superadmin has all the admin permissions, an admin has all the moderator ones, and so on. You don't need to copy the same permissions everywhere. Inheritance uses add_principal, child group first, then parent group.
# Admin inherits from moderator, which inherits from support
add_principal group.admin group.moderator
add_principal group.moderator group.support
Inheritance also applies to denials. A deny set on group.support applies to the moderator, the admin and the superadmin.
The line
add_ace group.admin group.moderator allowcreates no inheritance. It gives the admin group an object named group.moderator, which does nothing. Inheritance always goes throughadd_principal.
The basic syntax
Four commands are enough. They go in server.cfg, one per line.
# Allow or deny a permission to a group or a player
add_ace <principal> <permission> <allow/deny>

# Add a player to a group
add_principal <identifier> <group>

# Make a group inherit from another (child, then parent)
add_principal group.admin group.moderator

# Remove a permission or an inheritance
remove_ace <principal> <permission> <allow/deny>
remove_principal <identifier> <group>
Typed in the server console, these commands take effect at once. They are gone after the next restart unless they are in server.cfg. The official FiveM documentation describes them too.
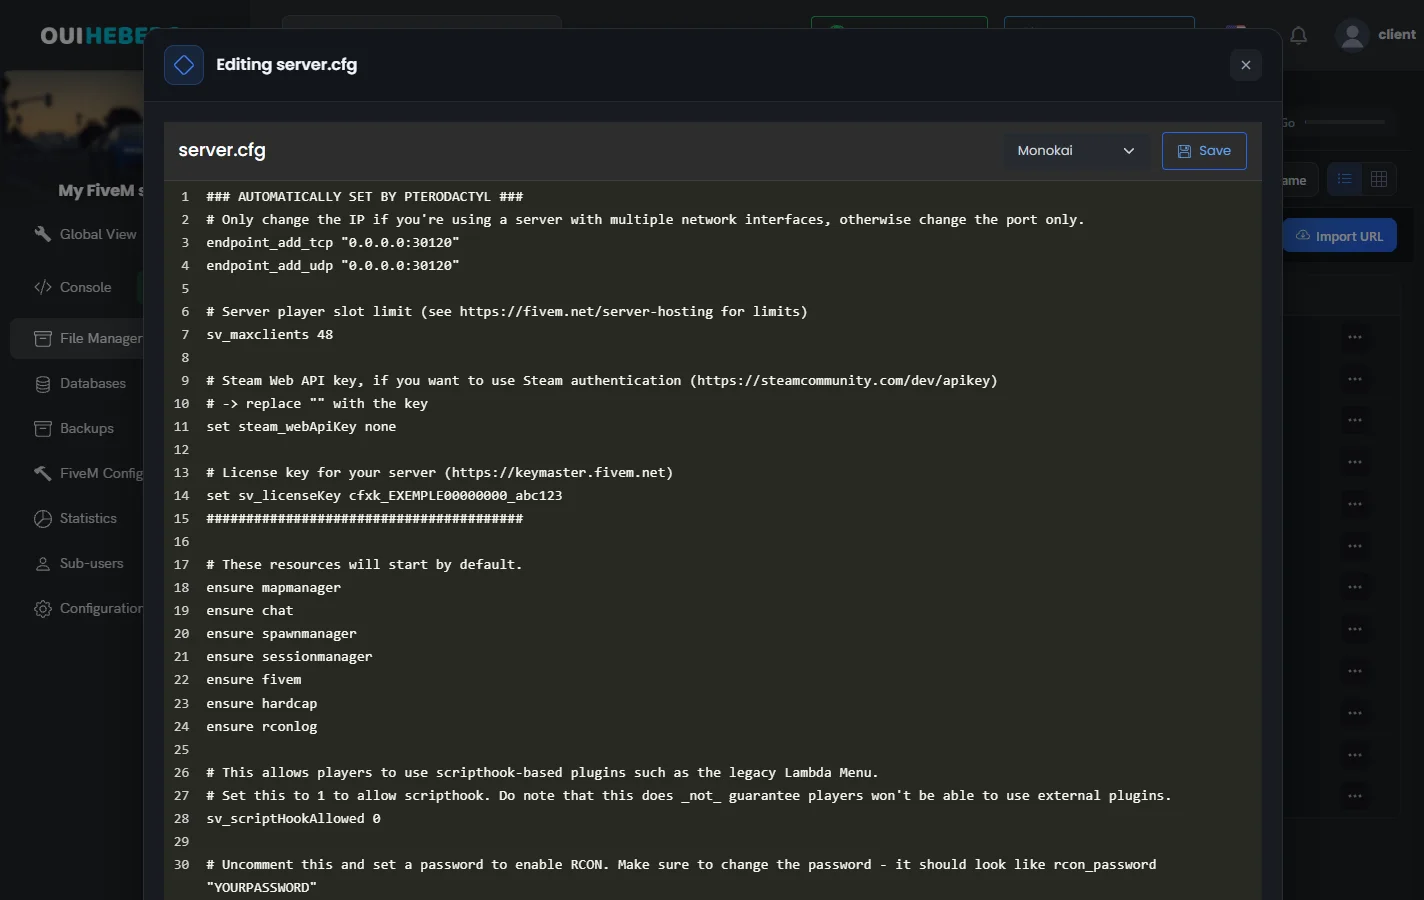
Open server.cfg in OuiPanel
The server.cfg file sits in the root folder of your server. You edit it in the OuiPanel File Manager.
Log in to OuiPanel at dash.ouipanel.com and open your server.
In the Console, stop the server with the Stop button.
In the side menu, click File Manager, then
server.cfg. The "Editing server.cfg" window opens.Add your permission lines, then click Save.
Restart the server from the Console.
Leave the lines under ### AUTOMATICALLY SET BY PTERODACTYL ###, at the top of the file, as they are. The panel writes them. The guide How to configure server.cfg on your FiveM server covers the rest of the file.
Simple configuration for a single admin
Just starting out and only want admin rights for yourself? Here is the minimum.
# Create the admin group with every command
add_ace group.admin command allow
# Except quit, which shuts the server down
add_ace group.admin command.quit deny

# Add yourself to the admin group (replace with your license)
add_principal identifier.license:xxxxxxxxxxxxxx group.admin
These are the lines of the official FiveM example. You get every command except quit. It is simple, but too coarse for a team. The next part splits rights across several groups.
Complete configuration: hierarchical structure
Here is a more serious setup, with four levels of rights and a VIP group. Each level inherits from the one below and adds its own commands.
####################################
# SUPERADMIN (server owner)
####################################

# Every command, plus the admin rights
add_ace group.superadmin command allow
add_principal group.superadmin group.admin
add_principal identifier.steam:110000xxxxxx group.superadmin

####################################
# ADMIN
####################################

# Admin inherits the moderator rights
add_principal group.admin group.moderator

# Admin-specific permissions
add_ace group.admin command.restart allow
add_ace group.admin command.stop allow
add_ace group.admin command.start allow
add_ace group.admin command.refresh allow
add_ace group.admin command.ensure allow
add_ace group.admin command.setjob allow
add_ace group.admin command.giveitem allow
add_ace group.admin command.givemoney allow
add_ace group.admin command.car allow
add_ace group.admin command.dv allow
add_ace group.admin command.tp allow
add_ace group.admin command.bring allow
add_ace group.admin command.unban allow

add_principal identifier.steam:110000yyyyyy group.admin

####################################
# MODERATOR
####################################

# Moderator inherits the support rights
add_principal group.moderator group.support

# Moderation permissions
add_ace group.moderator command.kick allow
add_ace group.moderator command.ban allow
add_ace group.moderator command.warn allow
add_ace group.moderator command.mute allow
add_ace group.moderator command.spectate allow
add_ace group.moderator command.goto allow
add_ace group.moderator command.announce allow

add_principal identifier.steam:110000zzzzzz group.moderator
add_principal identifier.discord:123456789 group.moderator

####################################
# SUPPORT
####################################

add_ace group.support command.tp allow
add_ace group.support command.tpto allow
add_ace group.support command.bring allow
add_ace group.support command.revive allow

add_principal identifier.steam:110000aaaaaa group.support

####################################
# VIP (perks without admin rights)
####################################

add_ace group.vip vip.priority allow
add_ace group.vip vip.customskin allow
add_ace group.vip vip.spawnvehicle allow

add_principal identifier.steam:110000bbbbbb group.vip
Commands such as setjob, car or revive come from your resources. They only exist if a resource registers them. The Steam identifiers in this example assume your players have linked a Steam account, as the next part explains.
Don't add a
denyonbuiltin.everyoneto protect restart, stop or exec. That denial would also hit your admins. A player has none of these commands anyway until you give them.
The different types of identifiers
A player is known by several identifiers. Each one is written identifier., then the type and the value. The GetPlayerIdentifiers page of the FiveM documentation lists every type.
Rockstar license (recommended)
The license comes from the player's Rockstar account, which FiveM requires. It is the safest identifier for your admins.
add_principal identifier.license:xxxxxxxxxxxxxx group.admin
Steam ID
The Steam identifier is still widely used. It only exists if the player has linked a Steam account to their Cfx.re account.
add_principal identifier.steam:110000xxxxxx group.admin
To require it from every player, add set sv_enforceSteamAuth true to server.cfg. A player without a linked Steam account will have to link one to join. This setting needs a server running build 38004 or later. It replaces steam_webApiKey, which has had no effect since November 4, 2026.
Discord ID
add_principal identifier.discord:123456789012345678 group.admin
To find it, turn on Developer Mode in the advanced settings of Discord. Then right-click the user and copy their ID.
FiveM ID
add_principal identifier.fivem:xxxxxx group.admin
This is the number of the player's Cfx.re account. The official FiveM example uses it to declare its first admin.
Identifying players by IP (
identifier.ip:xxx) is not recommended, because IP addresses change regularly.
Find a player's identifier
The status command, typed in the server console, lists connected players with their primary identifier, their number and their name. It comes from the rconlog resource, which must be started.
You can look up a Steam identifier on SteamID.io. FiveM expects its hexadecimal form, which starts with 110000.
Permissions for jobs (RP server)
On a roleplay server, you can create permissions for each job. Object names such as police.armory are up to you. They only do something if a script checks them.
# Police
add_ace group.police police.menu allow
add_ace group.police police.armory allow
add_ace group.police police.handcuff allow
add_ace group.police police.vehicle allow

# EMS
add_ace group.ems ems.menu allow
add_ace group.ems ems.vehicle allow
add_ace group.ems command.revive allow
add_ace group.ems command.heal allow

# Mechanic
add_ace group.mechanic mechanic.menu allow
add_ace group.mechanic mechanic.repair allow
A player joins a job group with add_principal, just like an admin. To grant every object that starts with police. at once, a single add_ace line is enough.
add_principal identifier.license:xxxxxxxxxxxxxx group.police
add_ace group.police police allow
In your server scripts, you then check the permission with IsPlayerAceAllowed.
if IsPlayerAceAllowed(source, 'police.armory') then
    -- The player can access the armory
end
This function only exists on the server side. Its reference page is in the FiveM natives list.
Restricting access to a resource
FiveM does not lock a whole resource away from a player. It controls what the resource offers, meaning its commands and the objects its scripts check.
A command that its script registers as restricted requires the command. permission followed by its name. In the script, this is the third argument of RegisterCommand.
-- Server script: the menuadmin command is restricted
RegisterCommand('menuadmin', function(source, args)
    -- opens the menu
end, true)
# Only admins can type /menuadmin
add_ace group.admin command.menuadmin allow
With false instead of true, everyone can use the command. For a menu without a command, the script must check an object itself with IsPlayerAceAllowed, as with jobs.
Give rights to a resource
The resource. principal followed by a name means the resource itself. You need it when a script has to run server commands. ESX needs it, for instance.
add_ace resource.es_extended command.add_principal allow
The lines
add_ace builtin.everyone resource.admin_menu denyandadd_ace group.admin resource.admin_menu allowprotect nothing. FiveM does not check a resource.admin_menu object on its own, and a deny on builtin.everyone also applies to your admins.
Permissions in txAdmin
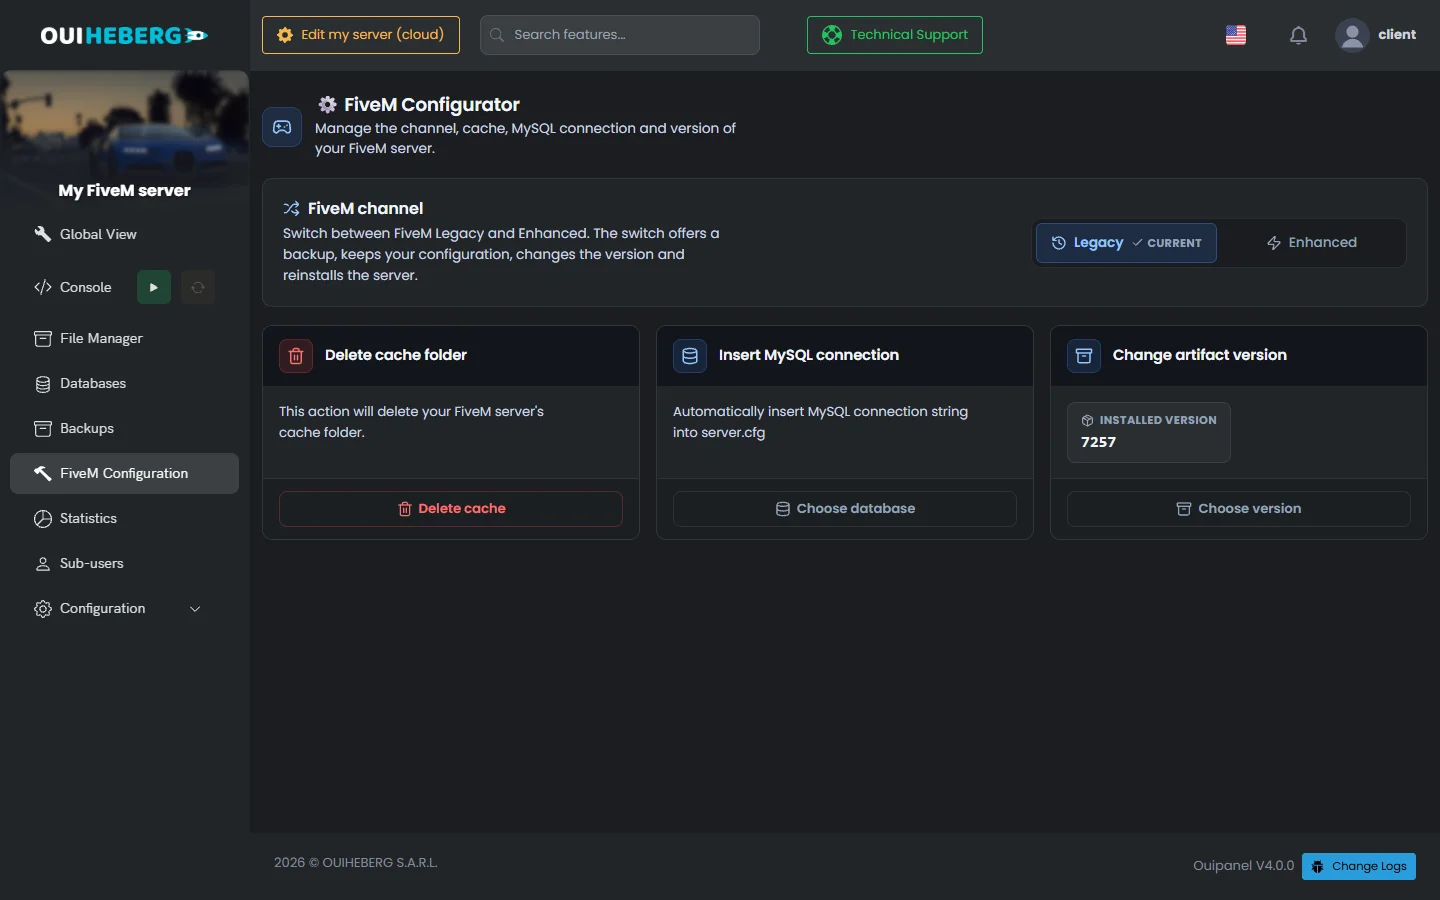
txAdmin, the FiveM web admin interface, only exists on the Legacy edition in OuiPanel. To check, click FiveM Configuration in the side menu. In the FiveM channel card, the Current badge must be on Legacy.
txAdmin does not use ACE. It has its own admin accounts and its own permissions, stored in txData/admins.json. You set them on its Admin Manager page. Lines such as add_ace group.superadmin txadmin allow change nothing there.
| txAdmin permission | What it allows |
|---|---|
all_permissions | Every action |
manage.admins | Create, edit and remove admin accounts |
console.view | View the console |
console.write | Type commands in the console |
control.server | Start, stop and restart the server |
commands.resources | Start and stop resources |
server.cfg.editor | Read and edit server.cfg |
players.kick | Kick a player |
players.ban | Ban or unban a player |
players.whitelist | Add a player to the whitelist |
The full list is in the txAdmin documentation. To turn on txAdmin and log in to it from OuiPanel, follow the guide Set up a FiveM whitelist with Discord and txAdmin.
Integration with ESX and QBCore
With ESX
ESX Legacy puts each player in a group stored in its database. When the player connects, ESX adds them to the ACE group of the same name, using their license. For this, server.cfg must allow es_extended to run these commands. These lines come with the server.cfg that ESX provides.
add_principal group.admin group.user
add_ace resource.es_extended command.add_ace allow
add_ace resource.es_extended command.add_principal allow
add_ace resource.es_extended command.remove_principal allow
add_ace resource.es_extended command.stop allow
You then give your commands to the admin group as usual.
add_ace group.admin command.setjob allow
add_ace group.admin command.givemoney allow
add_principal identifier.steam:xxx group.admin
Don't forget to also set the group to admin in the users table of your ESX database. ESX reads this group for its own checks.
With QBCore
QBCore declares its permission levels in qb-core/config.lua. By default, they are god, admin and mod. Each level matches a qbcore. principal followed by its name.
QBCore.Config.Server.Permissions = { 'god', 'admin', 'mod' }
The server.cfg that QBCore provides links these levels together. All that is left is to add yourself to the god level.
# Lines from the server.cfg provided by QBCore
add_ace resource.qb-core command allow
add_ace qbcore.god command allow
add_principal qbcore.god group.admin
add_principal qbcore.god qbcore.admin
add_principal qbcore.admin qbcore.mod

# Give yourself the god level (replace with your license)
add_principal identifier.license:xxxxxxxxxxxxxx qbcore.god
A god has every command and inherits the admin and mod levels. QBCore commands restricted to a level check these principals.
Useful commands for testing
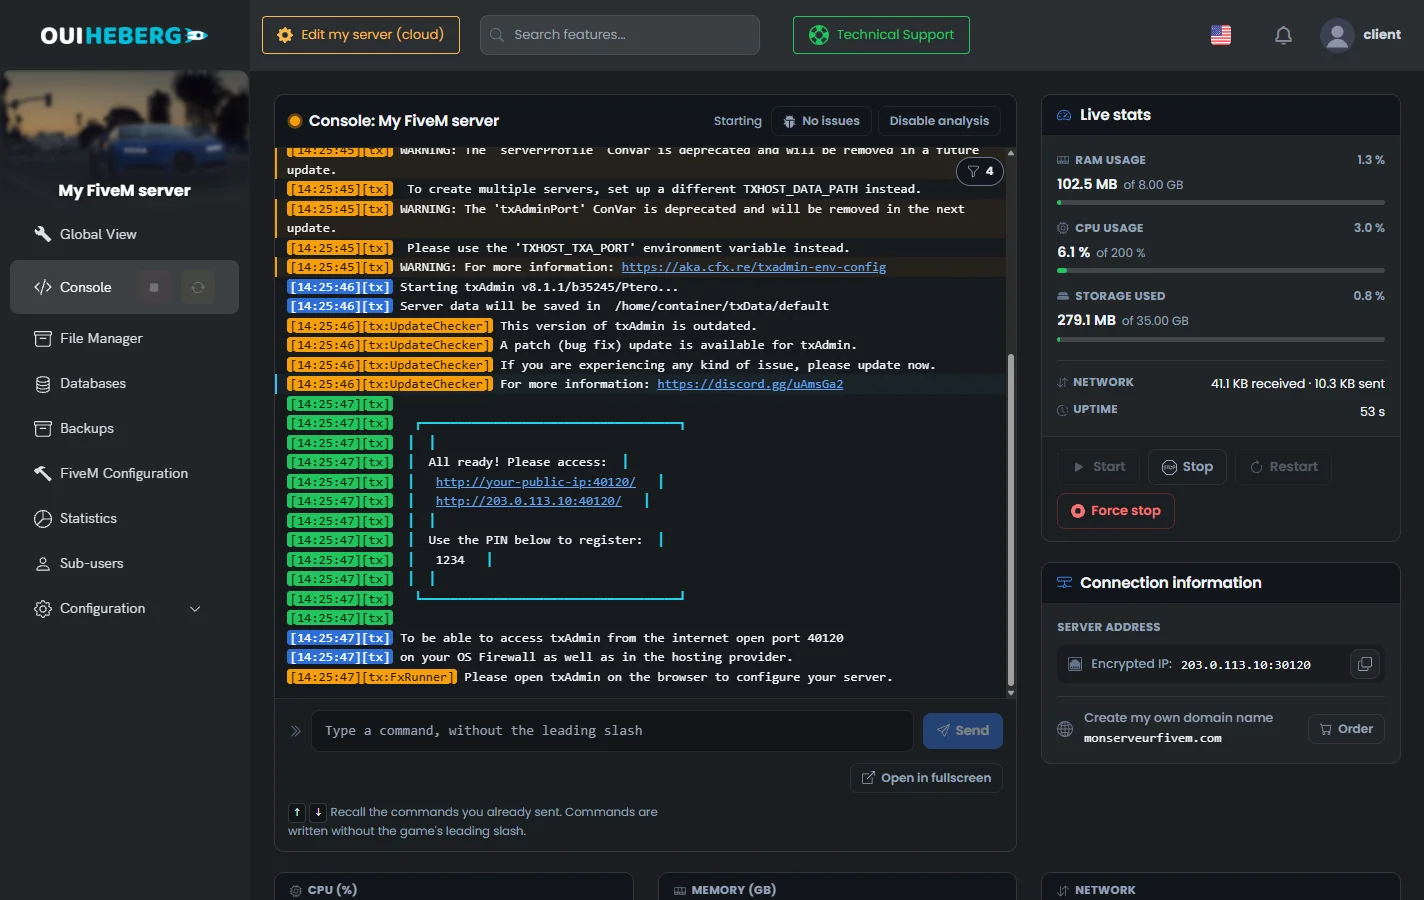
These commands are typed in the server console. In OuiPanel, open the Console, type the command in the "Type a command, without the leading slash" field, then click Send. In the in-game F8 console, they don't see the server's permissions.
Check if a player has a permission
test_ace identifier.steam:110000xxxxxx command.kick
The console answers true or false, in the form identifier.steam:110000xxxxxx -> command.kick = true. The first argument is a full principal, with identifier. in front. The player does not need to be connected. You can also test a group, with test_ace group.admin command.kick.
List all active permissions
list_aces
list_principals
list_aces shows each rule, such as group.admin -> command = ALLOW. list_principals shows inheritances and group members, such as group.admin <- group.moderator.
Trace every check
set se_debug true
The console then prints the result of every permission check. Run set se_debug false once you have found the problem, because the console fills up fast.
Resolving common issues
Permissions not applying
Fully restart the server.
refreshonly rescans the resources, notserver.cfg.Check every identifier. It needs the
identifier.prefix and the right type (license:,steam:,discord:). Case, on the other hand, does not matter.Use
statusto see the identifiers of connected players, then test the line withtest_ace.A script may read rights only once, when the player connects. When in doubt, have the player reconnect.
Line order does not matter
You can write add_principal before or after add_ace. FiveM checks rights when the player acts, once the whole file has been read. These two blocks give the same result.
# Player declared before the group
add_principal identifier.steam:xxx group.admin
add_ace group.admin command allow

# Group declared before the player
add_ace group.admin command allow
add_principal identifier.steam:xxx group.admin
An admin is refused despite their group
Look for a deny that applies to them with list_aces. A denial set on builtin.everyone, or on a group they inherit from, beats all their allow rules. Lines like these block everyone, admins included. Remove them.
add_ace builtin.everyone command.restart deny
add_ace builtin.everyone command.stop deny
add_ace builtin.everyone command.exec deny
Conflict with ESX/QBCore
If a command is refused despite the right ACE permissions, the script itself may have its own checks. Look at the configuration of that script.
Best security practices
Principle of least privilege
Only give the permissions that are strictly needed.
# Too broad
add_ace group.moderator command allow

# Precise
add_ace group.moderator command.kick allow
add_ace group.moderator command.ban allow
add_ace group.moderator command.warn allow
Protect critical commands
Keep restart, stop and exec for the top group. Avoid giving command as a whole to a group that others inherit from. If you do it anyway, take the dangerous commands away from it with a deny set on that group. This denial will also hit the groups that inherit from it.
# Only allow superadmins
add_ace group.superadmin command.restart allow
add_ace group.superadmin command.stop allow
Document your configuration
Comment your server.cfg so you can find your way around it.
# ===== ADMIN GROUP =====
# Can manage players and resources
# Can NOT stop/restart the server
add_ace group.admin command.kick allow
# ...
Need help?
Open a ticket from Tickets › Open a Ticket, or from the Contact support tile at the bottom of your server's page in the client area. You can also ask your question on the OuiHeberg Discord.
Discover our GTA V / FiveM hosting plans starting from $3.46/month, with your server ready in 60 seconds.
View plans →