 Client area

France
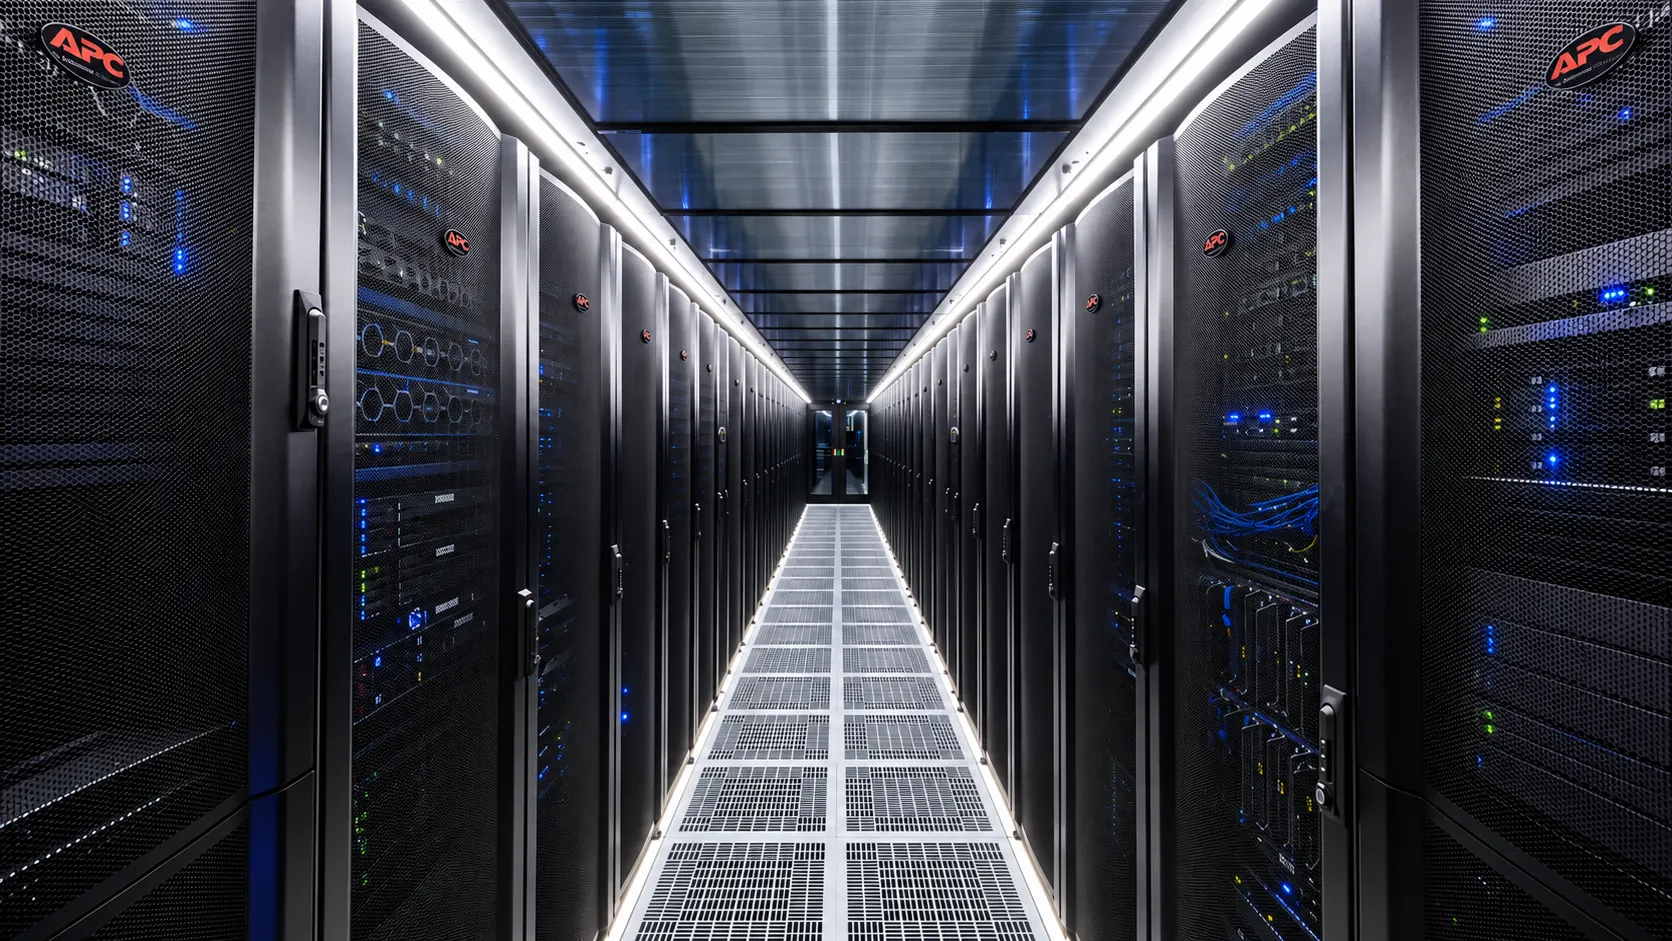
Digital Realty Marseille MRS1-3Landing point of the submarine cables to Africa, the Middle East and Asia. Minimal latency to France, Spain and Italy.
Peering: France-IX
Announce your prefixes on our network, over a fibre cross-connect or a GRE tunnel, in Marseille, Frankfurt or Amsterdam. Traffic is scrubbed upstream, before it reaches your equipment. Quote within 24 hours, no commitment.
Three choices are enough to frame the offer. The rest is settled with a network engineer, within 24 hours.
Location
Delivery mode
Committed bandwidth1 Gbps
BGP session
The three sites are interconnected on our backbone and protected by the same mitigation infrastructure.
Landing point of the submarine cables to Africa, the Middle East and Asia. Minimal latency to France, Spain and Italy.

The largest Internet exchange in the world. International connectivity and redundancy for services exposed to northern and eastern Europe.

At the heart of one of Europe's largest Internet hubs. Low latency to the Benelux, the United Kingdom and Scandinavia.
Many customers start on GRE to validate, then move to a cross-connect when traffic justifies it. Both can coexist.
Detection runs permanently on our border routers. As soon as an anomaly exceeds your traffic profile, the targeted prefix is diverted to the scrubbing centres, legitimate traffic keeps flowing, and your links never see the attack. No action on your side, no downtime.
Default profiles for web, gaming and VoIP. Custom rules on request, based on ports, rates and the geography of your traffic.
Full table or default route, IPv4 and IPv6, communities to steer your announcements. No ASN? We help you with the RIPE NCC.
Redundant transit and peering at the main exchange points. An upstream outage is invisible to you.
Committed rate, increased on demand without a new contract.
Traffic graphs and real-time alerts. Public Looking Glass access.
Contractual commitment on link availability.
No first-level support: you talk to the team that runs AS208226, day and night.
You have racks in Marseille, Frankfurt or Amsterdam and want protected transit without building your own mitigation.
Game and voice servers facing daily attacks: gaming DDoS profiles, stable latency.
Internet breakout for a head office or private data centre, with your own IPs and an SLA.
Quality of service and SIP/RTP flood filtering, with no added jitter.
You describe the need (above or through the contact form). An engineer calls you back.
Detailed proposal within 24 hours: bandwidth, mode, site, SLA. No commitment.
Cross-connect ordered from the data centre (under 48 hours) or GRE tunnel configured with your IPs (a few hours).
Session established, prefixes announced, mitigation active. Monitoring access.
BGP, mitigation, delivery, pricing.
It is the service that connects your infrastructure to the whole Internet through our network. We announce your routes to carriers and exchange points from Marseille, Frankfurt and Amsterdam, with built-in DDoS protection and guaranteed bandwidth.
Shared mitigation up to 3 Tbps, automatic and in real time. Volumetric attacks are filtered upstream, with no intervention and no downtime. Custom rules can be defined according to your traffic profile.
Yes, full table or default route, IPv4 and IPv6. Without an ASN or address block, our team helps you through the process with the RIPE NCC.
The cross-connect is a dedicated physical link in the data centre, with minimal latency and maximum bandwidth, for production. GRE is virtual, deployable in a few hours from anywhere, for tests, POCs or an immediate start. You can move from one to the other.
A few hours with GRE. Less than 48 hours for a fibre cross-connect after approval, the time needed to provision the link in the data centre.
By quote, based on committed bandwidth, delivery mode and site. Detailed proposal within 24 hours, no commitment. Bandwidth can then grow on demand, with a 99.9% SLA minimum.
Host your servers in our Marseille data center, at Digital Realty MRS2.
Physical machines delivered with 3 Tbps DDoS protection and guaranteed bandwidth.
Announce your own IPv4 and IPv6 prefixes from a VPS, on the AS208226 network.
Digital Realty MRS1-3, Equinix FR5, Digital Realty AMS5: who we are and where we operate.
Free quote within 24 hours, no commitment. Send your ASN and prefixes, we come back with a proposal and a schedule.